Penetration Testing
AI-enabled testing with every finding validated and exploited by accredited engineers.
- Web application testing
- API security testing
- Mobile app security (iOS & Android)
- Network & Active Directory
Every finding validated by accredited experts.
Trusted by security-conscious teams

Testing and consultancy delivered by CREST accredited professionals to protect your most valuable assets.
AI-enabled testing with every finding validated and exploited by accredited engineers.
Attack paths through your cloud estate and the AI features you ship.
Objective-based adversary simulation against your people, process and technology.
Get audit-ready, with every control mapped to the evidence your assessor asks for.
Continuous visibility of weaknesses, prioritised by what is actually exploitable.
Senior guidance to design, prioritise and run your security programme.
Penetration testing client
Customers
“The thoroughness of their pen test report was really helpful for us to understand how to remediate issues and see what the issues were and how we can recreate them on our end.”
Rankin D.Verified reviewer · Bonsai Data
Verified review on G2
Partners

Book a call for CREST-accredited penetration testing at a fixed, fair price.
Book a callFrom the first exploit to a clean bill of health, with an accredited engineer on every step.
Prove exploitability with real attacks.
AI maps your attack surface at speed. Accredited engineers then validate, chain and exploit what it finds, so you see real attack paths, not scanner noise.
Prioritise what actually matters.
Every finding arrives CVSS-scored, mapped to your controls and Jira-ready, with reproduction steps and the fix your engineers need. Criticals are flagged within 24 hours.
Suggested fix · SEC-142
- if (token.valid) resetPassword(user)
+ if (token.valid && !token.used) {
+   await token.markUsed(); resetPassword(user)
+ }
Verify every fix, free.
Once you have remediated, we re-run each exploit to confirm it is closed. Retesting is included in every engagement.
Every fix re-exploited and verified by a senior engineer.
Show auditors a clean bill of health.
You receive a clean health report and updated attestation, ready for your board, your customers and your auditor.
 CyberFortifySecurity Health Report
Customer portal & public API
The people accountable for every engagement.
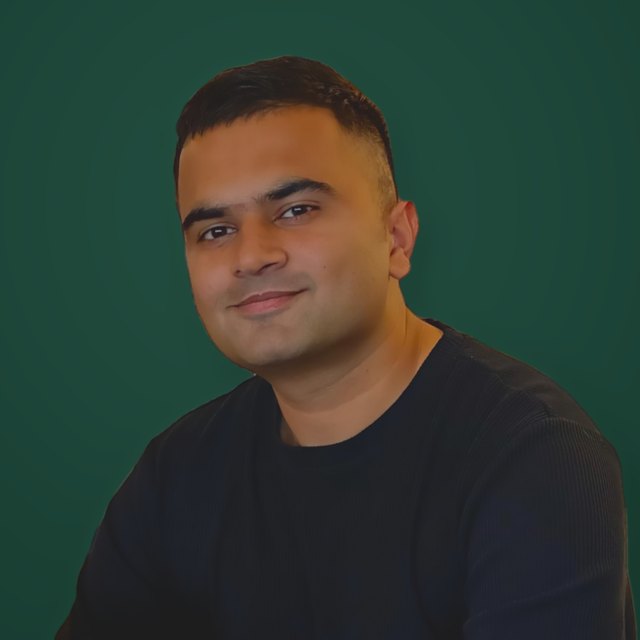
CEO & Founder
Leads every engagement, with five years of hands-on testing across SaaS, fintech and healthcare.
Book a call with Usama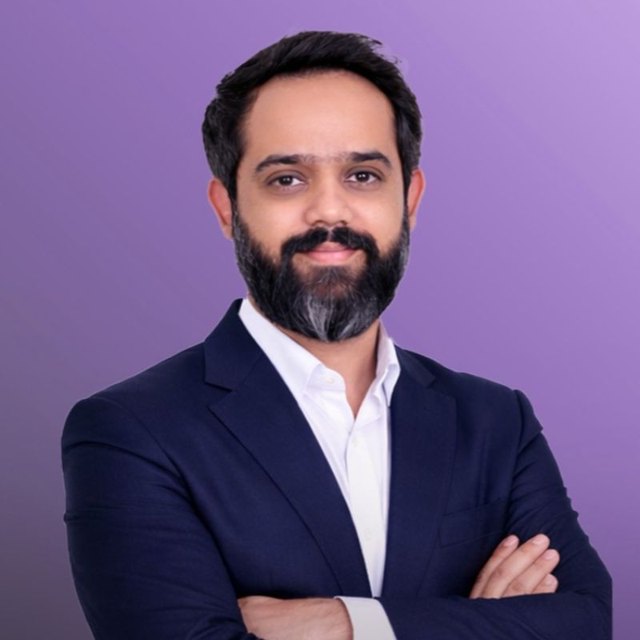
CEO & Advisor
Guides CyberFortify's growth and the partnerships that extend our reach to new markets.
CyberFortify on LinkedInTeams across four countries, testing for clients worldwide. Engagements run remotely, so your location never limits who tests you.
 Bahrain
 United States
 United Kingdom
 Uzbekistan
 BahrainUnited StatesUnited KingdomUzbekistan
Send us a message, or talk to Usama directly.
Your first call is with Usama Gul, our founder and the engineer who leads your test. You’ll leave with a clear scope and a fixed price.